
Welcome:
Login
|
Sign Up
|
About CircleID
Follow:
|
|

|
||
|
||
CloudSEK recently uncovered a global Microsoft 365 PhaaS operation that targeted hundreds of organizations across 40+ countries they dubbed “BigBear 2.0.” Their investigation exposed the attacker’s admin panel, affiliate network, phishing infrastructure, and thousands of stolen credentials and session cookies, thus revealing how modern AiTM attacks can hijack sessions even if authenticated via MFA.
The researchers identified 48 network IoCs made up of a subdomain, domains, and IP addresses. After extracting unique domains and verifying their ownership legitimacy aided by the WhoisXML API MCP Server, we ended up with a subdomain, 12 domains, and 25 IP addresses, totaling 38 network IoCs, for our analysis.
In the end, our deep dive into the threat led to these discoveries:
A sample of the additional artifacts obtained from our analysis is available for download from our website.
We began our analysis by querying the sole subdomain IoC on the WhoisXML API MCP Server. We found out that management[.]michaelmarcotte[.]com was first seen on 29 June and last seen on 21 July 2026. And while it did not have Threat Intelligence API hits, it seemed to be part of a 29 June 2026 burst of lookalike auth subdomains beginning with login, mysignins, account, portal, or device according to an analysis of the apex domain. It resembles IoCs connected to credential phishing or fake admin panel staging.
We also learned that there were 18 other subdomains under the apex domain michaelmarcotte[.]com. The www, mail, cpanel, webmail, webdisk, cpcalendars, cpcontacts, ftp, and whm subdomains looked to be legitimate cPanel or hosting infrastructure components first seen between 2017 and 2025. The management, device, login, mysignins, account, portal, honey, cloudfront, cdn, and vn3hg subdomains, meanwhile, all first seen on 29 June 2026, were suspicious as stated earlier.
Next up, we zoomed in on the 12 domain IoCs.
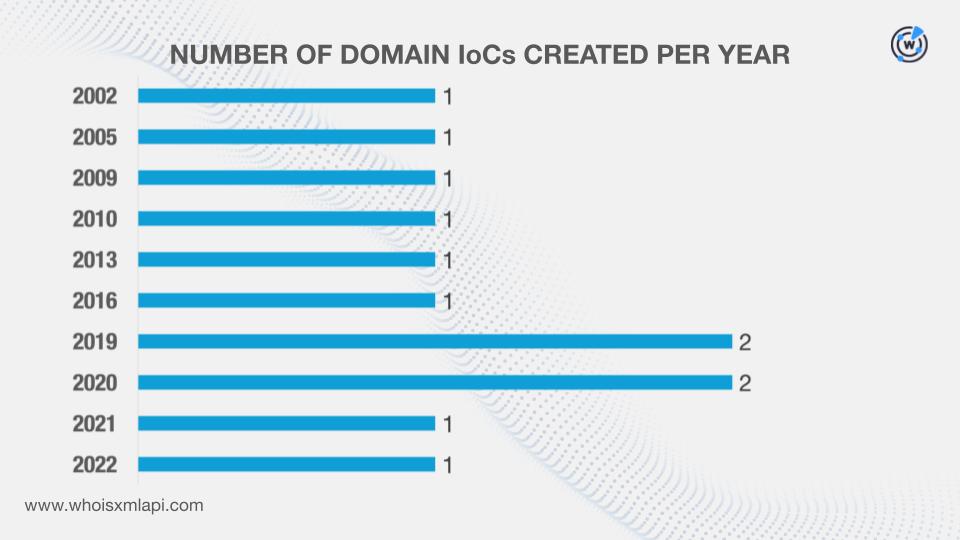
We started by querying them on WHOIS API and discovered that:
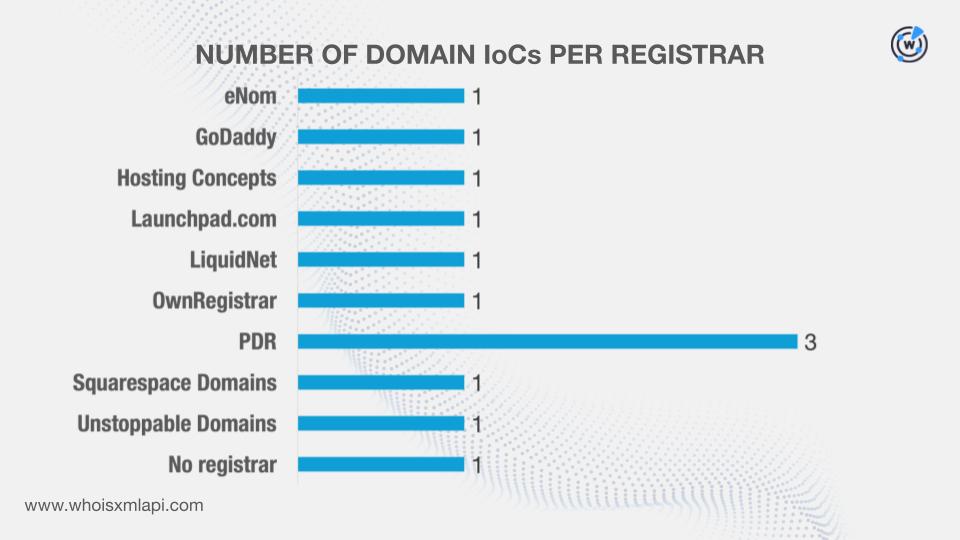
While one did not have a registrar on record, the remaining 11 were administered by nine registrars.
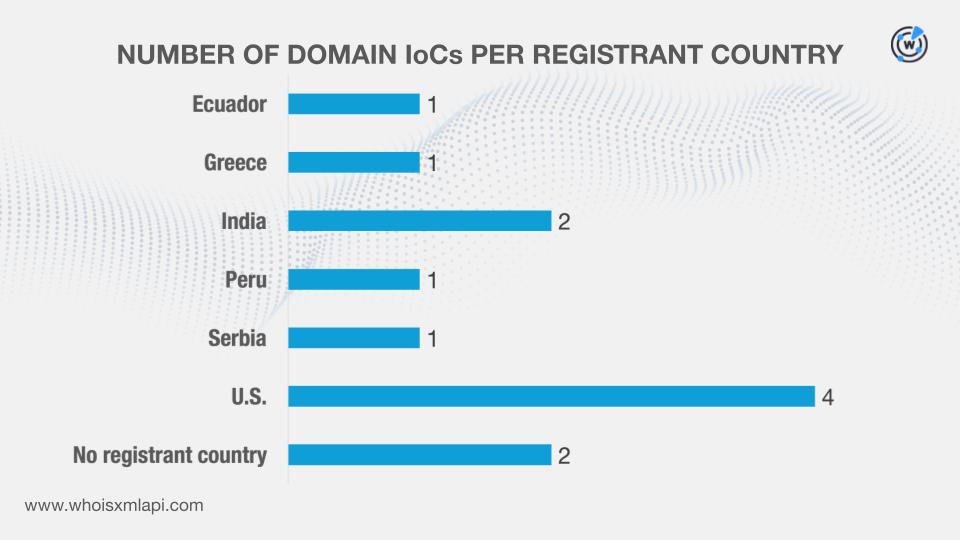
While two did not have registrant countries on record, the remaining 10 were registered in six countries.
We then queried the domain IoCs on DNS Chronicle API and found out that they recorded 3,230 historical domain-to-IP resolutions over time. Here are more details for five examples.
| DOMAIN IoC | NUMBER OF DOMAIN-TO-IP RESOLUTIONS | DATES SEEN |
|---|---|---|
| konceptenterprises[.]com | 410 | 02/06/17–09/04/26 |
| michaelmarcotte[.]com | 406 | 02/06/17–09/04/26 |
| kgsscans[.]com | 402 | 07/29/17–08/19/26 |
| planisteradmin[.]com | 396 | 02/06/17–08/17/26 |
| haliotisbar[.]com | 312 | 02/05/17–08/25/26 |
Next, we zoomed in on the 25 IP IoCs.
We learned from sample network traffic data from the IASC that 81 unique IP addresses potentially owned by victims communicated with 18 of the IP IoCs. These IPs fell under 17 distinct ASNs.
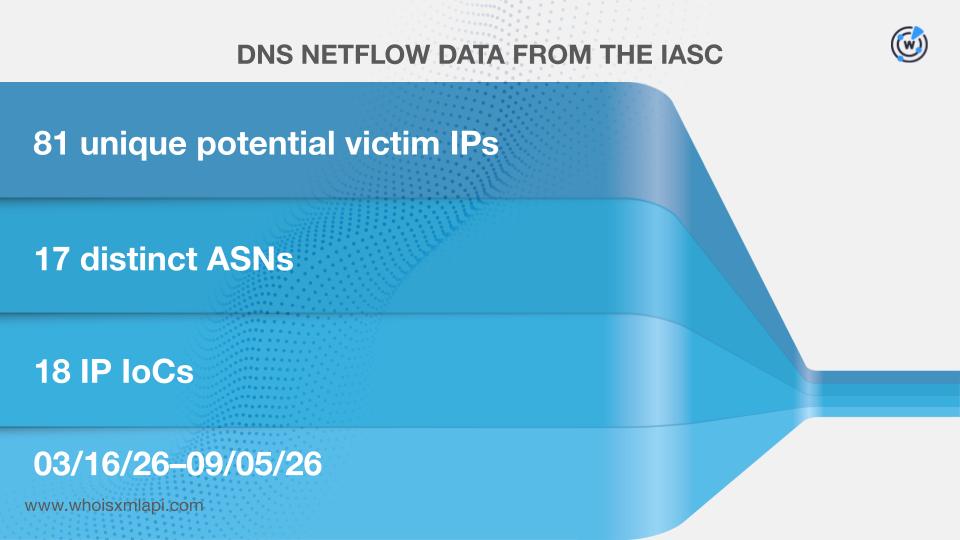
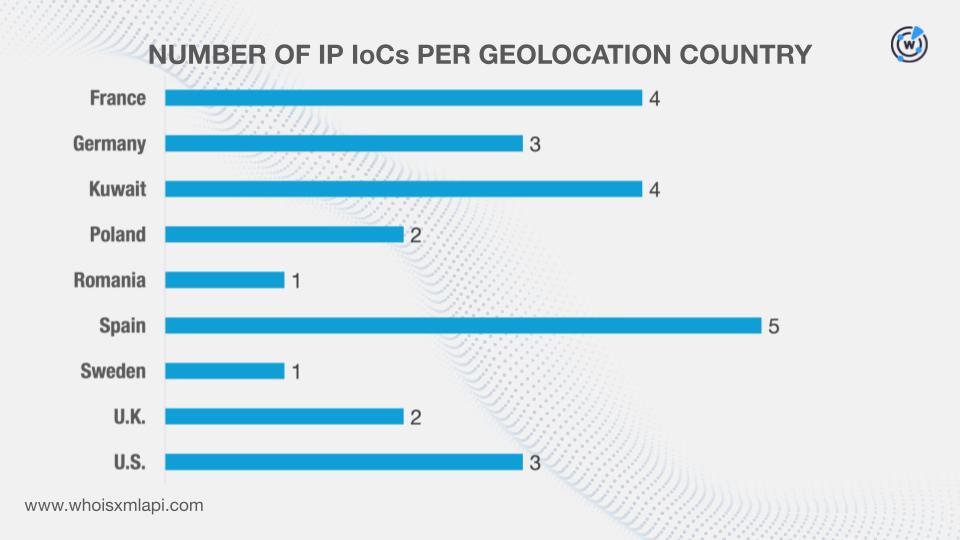
We then queried the IP IoCs on Bulk IP Geolocation Lookup and discovered that:
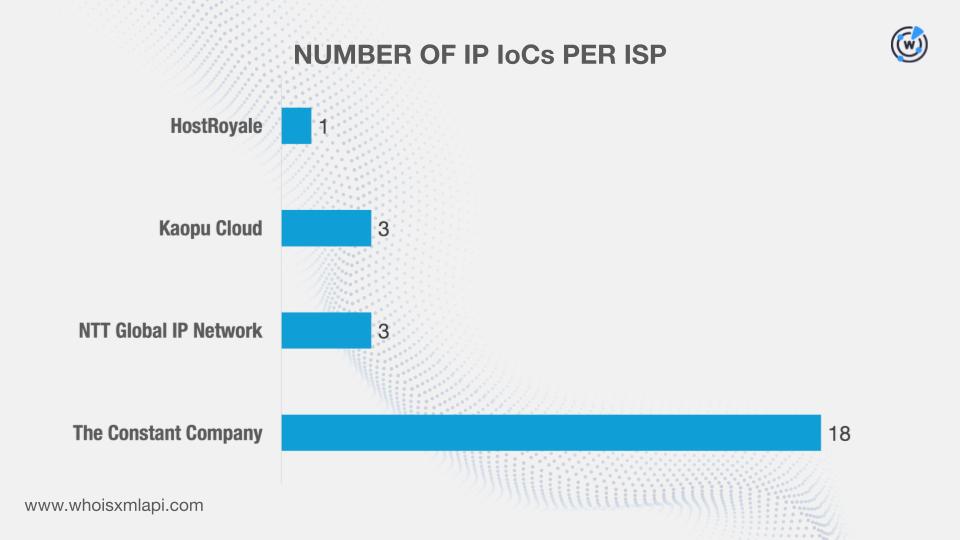
They were administered by four ISPs.
When queried on DNS Chronicle API, we found out that 22 of the IP IoCs posted 1,012 historical IP-to-domain resolutions over time. Here are more details for five examples.
| IP IoC | NUMBER OF IP-TO-DOMAIN RESOLUTIONS | DATES SEEN |
|---|---|---|
| 199[.]247[.]10[.]14 | 206 | 10/09/19–08/30/26 |
| 70[.]34[.]244[.]122 | 98 | 07/31/20–09/05/26 |
| 65[.]20[.]103[.]58 | 85 | 05/21/26–09/03/26 |
| 107[.]191[.]46[.]14 | 81 | 06/28/22–09/03/26 |
| 95[.]179[.]233[.]79 | 69 | 04/01/20–07/26/26 |
After unearthing more information about the IoCs, we then hunted for other connected artifacts.
First, we queried the domain IoCs on WHOIS History API and learned that 12 of them had 65 unique email addresses in their historical records. Of these, 16 were public email addresses.
Reverse WHOIS API queries for the public email addresses led to the discovery of 1,048 unique email-connected domains after those already dubbed as IoCs were filtered out. And based on the Threat Intelligence API results we obtained, futureoneenterprises[.]com has already figured in phishing campaigns seen on 22 July 2026.
We queried the email-connected domains on Domain Traffic API next and determined the 10 most visited ones.
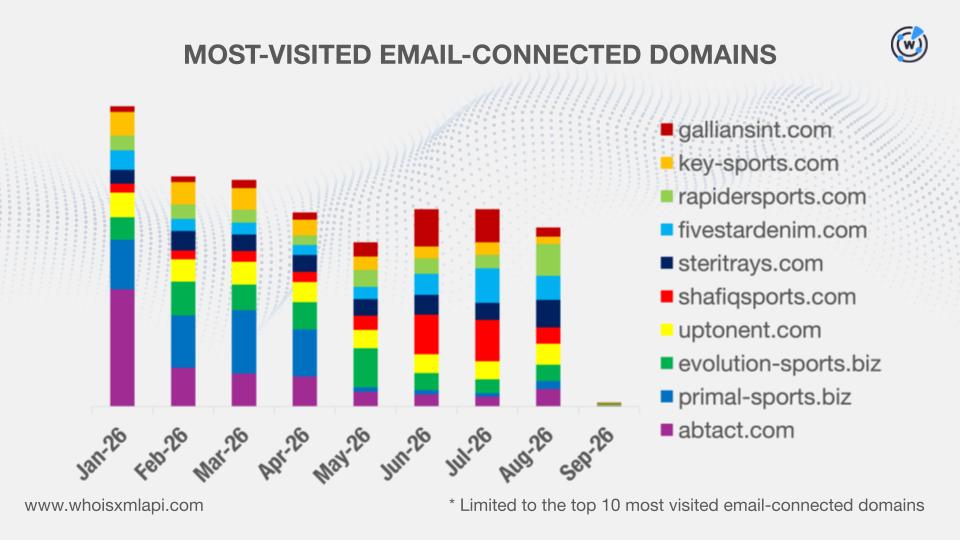
Here are more details about the said domains.
| EMAIL-CONNECTED DOMAIN | JAN | FEB | MAR | APR | MAY |
|---|---|---|---|---|---|
| abtact[.]com | 318,452 | 105,188 | 89,455 | 81,831 | 40,038 |
| primal-sports[.]biz | 134,851 | 142,409 | 172,591 | 127,743 | 12,254 |
| evolution-sports[.]biz | 60,737 | 91,772 | 69,417 | 73,915 | 105,903 |
| uptonent[.]com | 66,792 | 60,496 | 61,837 | 54,878 | 49,908 |
| shafiqsports[.]com | 24,847 | 23,925 | 28,941 | 27,417 | 38,606 |
| steritrays[.]com | 36,960 | 53,429 | 45,419 | 45,649 | 44,993 |
| fivestardenim[.]com | 53,515 | 32,405 | 31,675 | 27,456 | 33,712 |
| rapidersports[.]com | 39,927 | 39,694 | 35,506 | 26,236 | 46,172 |
| key-sports[.]com | 64,174 | 60,010 | 58,135 | 42,522 | 35,997 |
| galliansint[.]com | 15,315 | 16,144 | 22,496 | 19,569 | 38,405 |
| EMAIL-CONNECTED DOMAIN | JUN | JUL | AUG | SEP | TOTAL |
|---|---|---|---|---|---|
| abtact[.]com | 32,946 | 26,893 | 47,662 | 1,778 | 744,243 |
| primal-sports[.]biz | 12,036 | 10,115 | 21,870 | 1,123 | 634,992 |
| evolution-sports[.]biz | 46,159 | 37,189 | 43,952 | 1,443 | 530,487 |
| uptonent[.]com | 51,216 | 48,998 | 57,258 | 1,483 | 452,866 |
| shafiqsports[.]com | 107,173 | 112,462 | 44,259 | 1,143 | 408,773 |
| steritrays[.]com | 54,037 | 45,682 | 75,083 | 1,348 | 402,600 |
| fivestardenim[.]com | 56,966 | 94,486 | 65,180 | 0 | 395,395 |
| rapidersports[.]com | 42,345 | 36,414 | 85,974 | 1,955 | 354,223 |
| key-sports[.]com | 31,722 | 34,035 | 20,289 | 577 | 347,461 |
| galliansint[.]com | 101,417 | 90,062 | 24,710 | 491 | 328,609 |
We also identified the day when each email-connected domain recorded the highest number of visits.
This post only contains a snapshot of the full research. Download the complete findings and a sample of the additional artifacts on our website or contact us to discuss your intelligence needs for threat detection and response or other cybersecurity use cases.
Disclaimer: We take a cautionary stance toward threat detection and aim to provide relevant information to help protect against potential dangers. Consequently, it is possible that some entities identified as “threats” or “malicious” may eventually be deemed harmless upon further investigation or changes in context. We strongly recommend conducting supplementary investigations to corroborate the information provided herein.
Sponsored byWhoisXML API

Sponsored byRadix

Sponsored byVerisign

Sponsored byDNIB.com

Sponsored byIPv4.Global

Sponsored byCSC
Sponsored byVerisign
A World-Renowned Source for Internet Developments. Serving Since 2002.