
Welcome:
Login
|
Sign Up
|
About CircleID
Follow:
|
|

|
||
|
||
TrendAI Research uncovered a sustained spearphishing campaign targeting Ukrainian government agencies, defense organizations, border guard units, and logistics operators launched by the Russia-aligned intrusion set they track as Earth Sirrush, formerly SHADOW-EARTH-065 that overlaps with the UAC-0099 designation by the Computer Emergency Response Team of Ukraine (CERT-UA). They published a report that traced the group’s operations from 2022 to July 2026, which revealed their continuous malware replacement while retaining recognizable development, delivery, and infrastructure patterns.
The technical brief identified 52 network IoCs comprising one subdomain, six email addresses, 24 domains, and 21 IP addresses.
After determining the reported domain IoCs’ legitimacy using WHOIS API, Website Categorization API, and Threat Intelligence API via the WhoisXML API MCP Server, we excluded three from the list, ending up with 21 domain IoCs for our analysis. In sum, we investigated 49 network IoCs made up of one subdomain, six email addresses, 21 domains, and 21 IP addresses. We uncovered these findings in the end:
A sample of the additional artifacts obtained from our analysis is available for download from our website.
We kicked off our deep dive by zooming in on the sole subdomain IoC order[.]cyberflysystems[.]com.
Based on the results of our WhoisXML API MCP Server Subdomains Lookup API query, its apex domain had three other subdomains (i.e., www, mail, and ftp). Here are more details on the subdomains’ first and last seen dates.
| SUBDOMAIN | FIRST SEEN DATE | LAST SEEN DATE |
|---|---|---|
| www[.]cyberflysystems[.]com | 09/01/25 | 04/17/26 |
| mail[.]cyberflysystems[.]com | 01/20/26 | 04/17/26 |
| ftp[.]cyberflysystems[.]com | 01/20/26 | 04/17/26 |
| order[.]cyberflysystems[.]com | 04/16/26 | 04/16/26 |
We also learned that three of the apex domain’s historical IP addresses (i.e., 35[.]187[.]82[.]108, 135[.]181[.]41[.]169, and 65[.]108[.]39[.]53) were associated with malware distribution and phishing between 2023 and 2026.
Finally, the apex domain could be typosquatting on the cyberfly brand.
We then took a closer look at the six email address IoCs.
While all the IoCs had valid syntax, one did not have an MX record according to the results of our Email Verification API query via the WhoisXML API MCP Server. In addition, another IoC was used to register domains based on data from Reverse WHOIS API.
Next, we focused on the 21 domain IoCs.
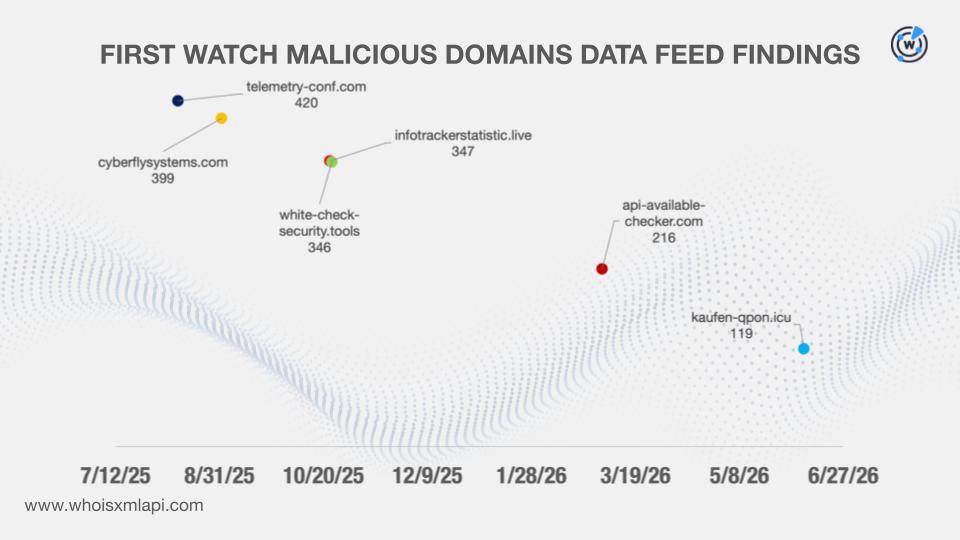
Data from the First Watch Malicious Domains Data Feed showed that six of the domain IoCs were likely registered with malicious intent 119–420 days before they were publicized as IoCs on 5 October 2026.
The results of our Bulk WHOIS API query with missing details provided by Domain Info API revealed that:
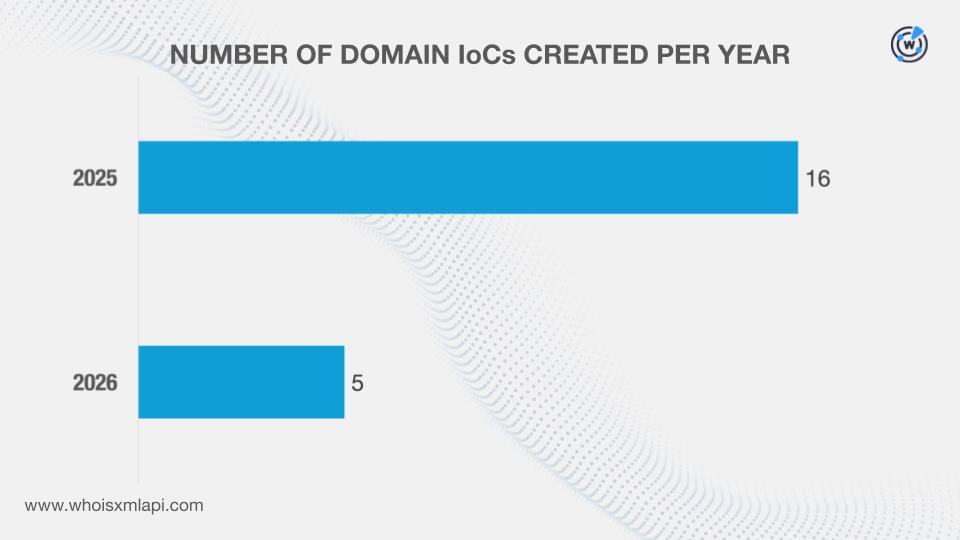
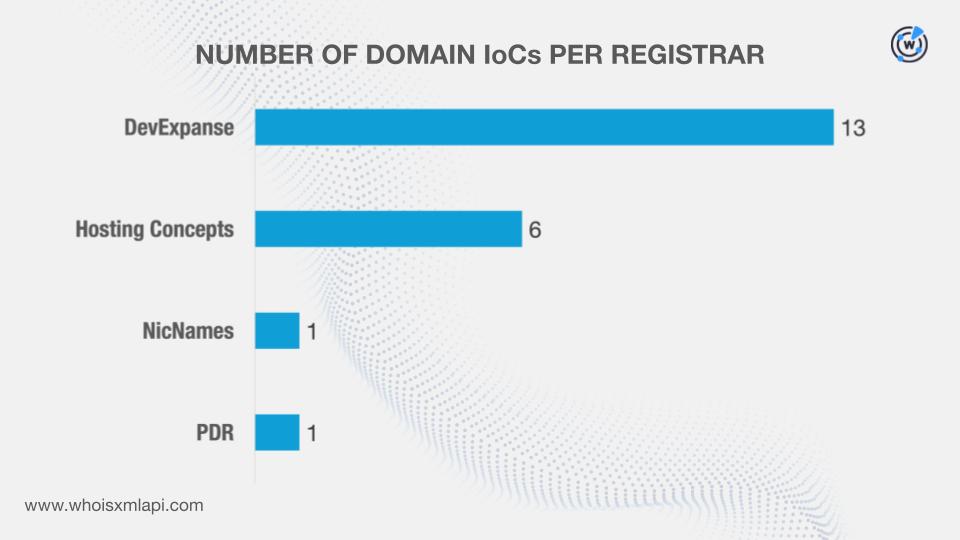
They were administered by four registrars.
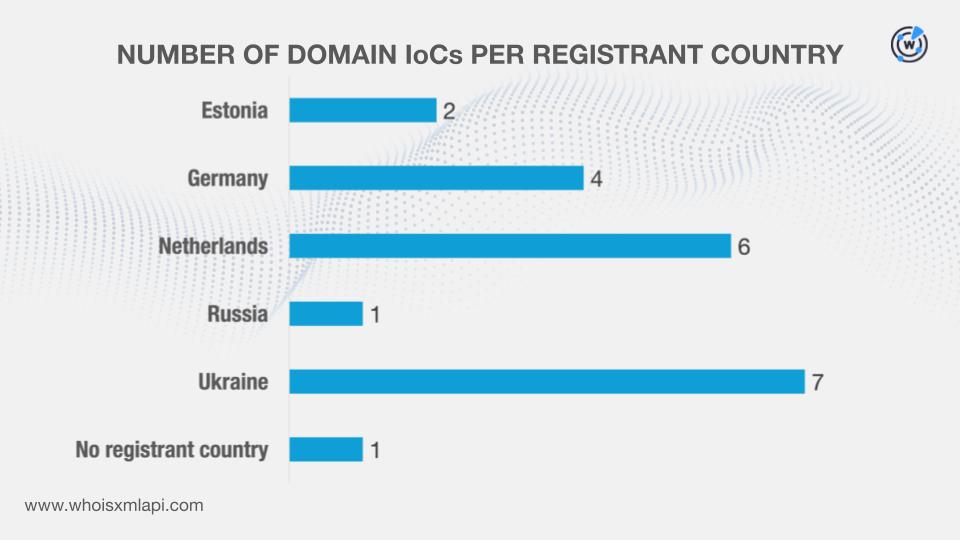
While one IoC did not have a registrant country on record, the remaining 20 were registered in five countries.
A DNS Chronicle API query for the IoCs revealed that they recorded 1,028 historical domain-to-IP resolutions since 29 April 2017. Take a look at more information for five examples below.
| DOMAIN IoC | NUMBER OF DOMAIN-TO-IP RESOLUTIONS | DATES SEEN |
|---|---|---|
| rutech[.]tech | 272 | 12/11/17–09/17/26 |
| startdeeplearning[.]com | 212 | 04/29/17–06/28/26 |
| uztickets[.]com | 132 | 04/29/17–06/28/25 |
| activation-planner[.]pro | 48 | 03/03/26–09/19/26 |
| virtualdailyplanner[.]pro | 44 | 11/10/25–09/16/26 |
Over time, three of the IoCs began resolving in 2017, 13 in 2025, and five in 2026.
Next, we focused on the 21 IP IoCs.
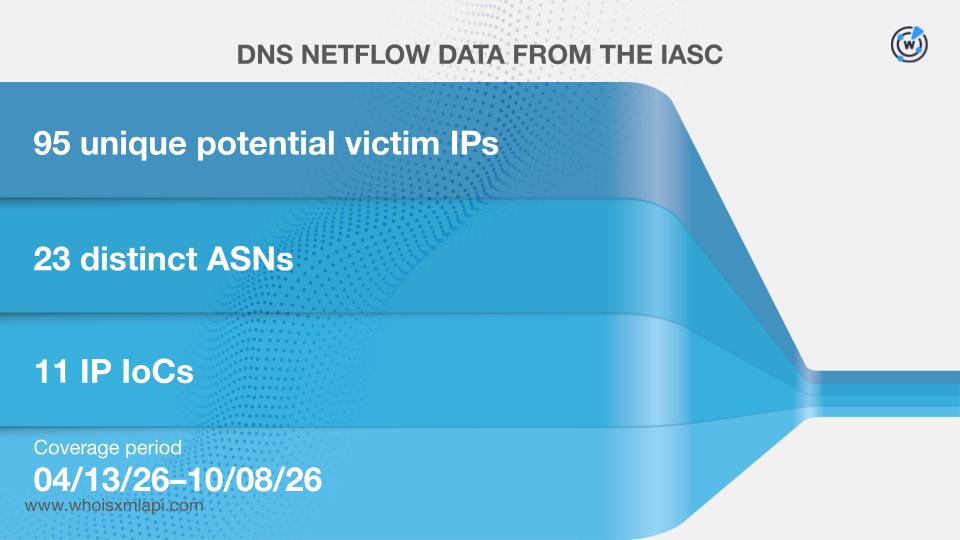
Sample network traffic data from the IASC revealed that 95 distinct IP addresses potentially owned by victims communicated with 11 of the IoCs.
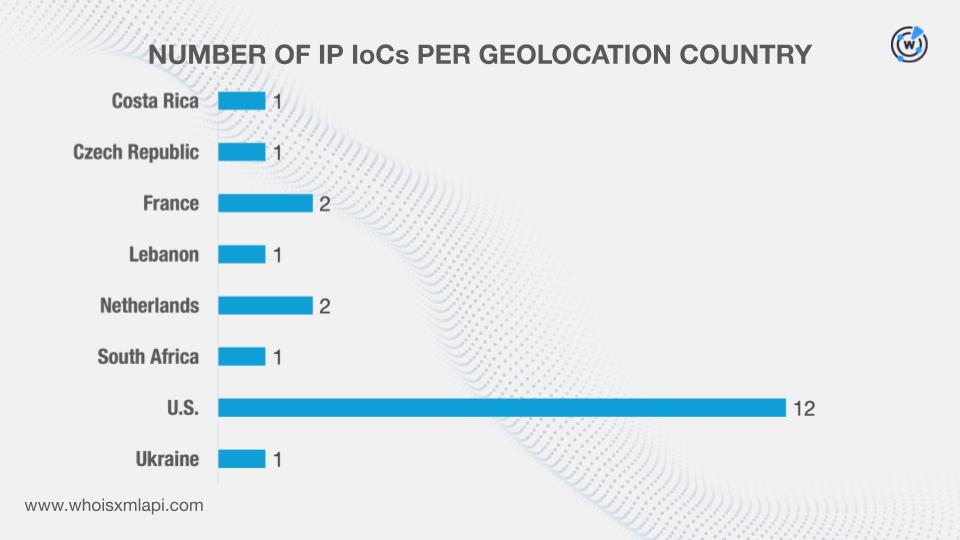
A Bulk IP Geolocation Lookup query for the IoCs also showed that:
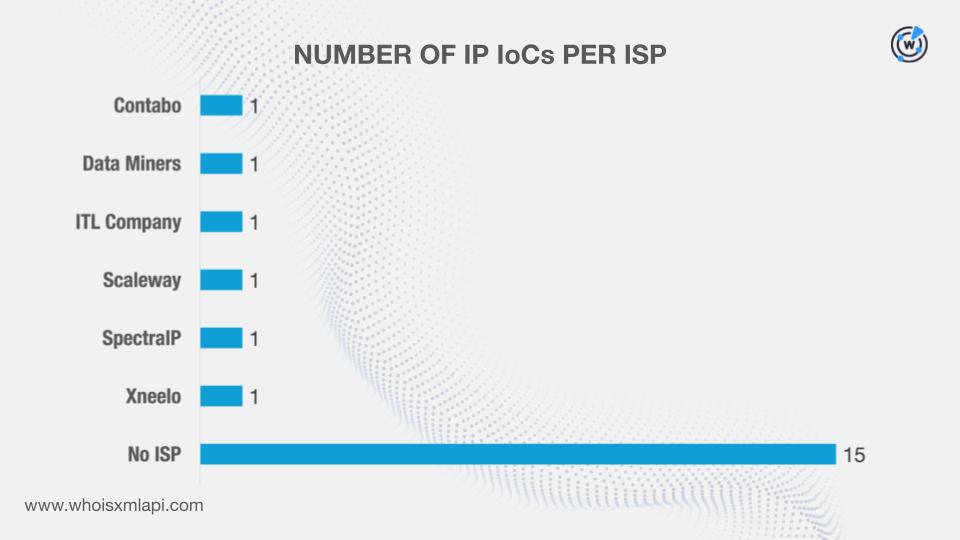
While 15 did not have ISPs on record, the remaining six were administered by the same number of companies.
We then queried the IoCs on DNS Chronicle API and discovered that 13 posted 3,761 historical IP-to-domain resolutions between 4 February 2017 and 5 October 2026. Here are more details for five examples.
| IP IoC | NUMBER OF IP-TO-DOMAIN RESOLUTIONS | DATES SEEN |
|---|---|---|
| 185[.]53[.]46[.]190 | 1,000 | 08/06/21–05/22/25 |
| 85[.]209[.]195[.]161 | 1,000 | 07/27/19–08/14/25 |
| 95[.]111[.]249[.]30 | 1,000 | 05/29/20–09/24/25 |
| 62[.]210[.]204[.]94 | 562 | 02/04/17–08/01/24 |
| 64[.]95[.]13[.]21 | 102 | 04/22/24–06/05/26 |
Over time, one IoC each started resolving in 2017, 2019, 2020, and 2023; two each in 2021 and 2025; and five in 2024.
To gather possibly connected artifacts not on TrendAI’s list, we queried the domain IoCs on WHOIS History API. We learned that four had 11 unique email addresses in their historical records.
Upon closer examination, five were public email addresses. And since we determined earlier that one of the email IoCs served as a registrant email address, we collated six public email addresses for the next step.
A Reverse WHOIS API query for the public email addresses led to the discovery of 283 unique email-connected domains after the domain IoCs were filtered out.
When queried on Domain Traffic API, we learned that 12 email-connected domains recorded visits since 1 January 2026.
This post only contains a snapshot of the full research. Download the complete findings and a sample of the additional artifacts on our website or contact us to discuss your intelligence needs for threat detection and response or other cybersecurity use cases.
Disclaimer: We take a cautionary stance toward threat detection and aim to provide relevant information to help protect against potential dangers. Consequently, it is possible that some entities identified as “threats” or “malicious” may eventually be deemed harmless upon further investigation or changes in context. We strongly recommend conducting supplementary investigations to corroborate the information provided herein.
Sponsored byRadix

Sponsored byVerisign

Sponsored byCSC
Sponsored byDNIB.com

Sponsored byWhoisXML API

Sponsored byVerisign
Sponsored byIPv4.Global

A World-Renowned Source for Internet Developments. Serving Since 2002.