
Welcome:
Login
|
Sign Up
|
About CircleID
Follow:
|
|
|

|
||
|
||
Google Threat Intelligence Group (GTIG) recently published a report on three Russian threat groups—UNC6293, UNC7005, and UNC5976—targeting various persons of interest for the country. They identified 32 network IoCs comprising two subdomains, 25 domains, and five IP addresses.
We extracted two domains from the subdomain IoCs, ending up with 27 in total. We then weeded out those that belonged to legitimate companies aided by the WhoisXML API MCP Server, trimming down the number to 26 domains. All in all, we analyzed 33 network IoCs made up of two subdomains, 26 domains, and five IP addresses.
Our DNS deep dive into the threat led to these findings:
A sample of the additional artifacts obtained from our analysis is available for download from our website.
We kicked off our investigation by zooming in on the two subdomain IoCs. Based on the results of our analysis via the WhoisXML API MCP Server, we learned that one posed great risk while the other was rated moderately risky. Here are more details about them.
| SUBDOMAIN IoC | WXA MCP SERVER FINDING |
|---|---|
| drive[.]google[.]verify-drive[.]com | High risk; deceptive subdomain labeling (drive[.]google as subsubdomain of verify-drive[.]com) to impersonate Google Drive; brand new; privacy-protected WHOIS record; low-reputation leased netblock; co-hosted with Google-mimicking domains |
| mail[.]kiis[.]co[.]uk | Moderate risk; dropped and reregistered domain with prior reputation; configured email-only via registrar forwarding; no website; KIIS brand-adjacent; low-reputation NSP host |
Overall, avoiding both subdomain IoCs may be warranted.
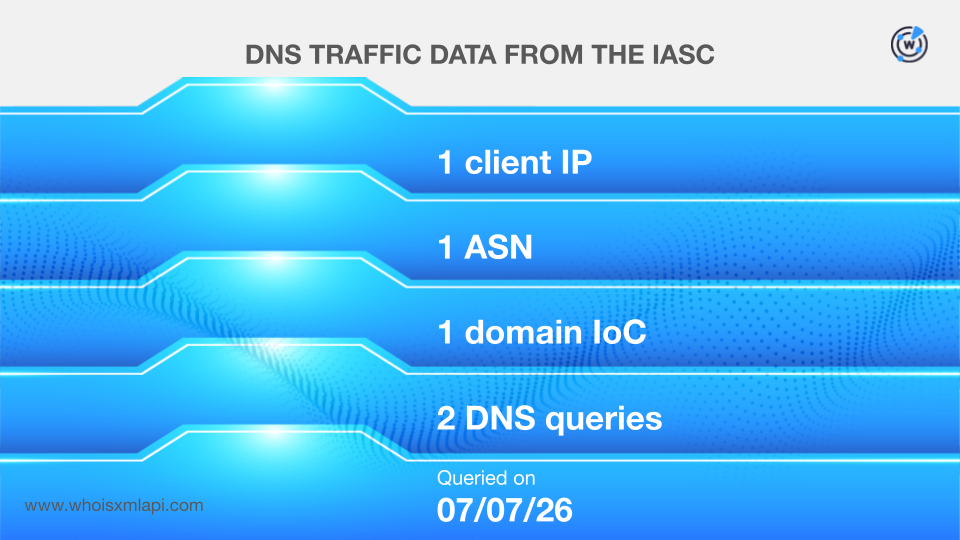
Next, we took a closer look at the 26 domain IoCs. Sample network traffic data from the IASC revealed that one client IP address communicated with the IoC globsec[.]net via two DNS queries on 7 July 2026.
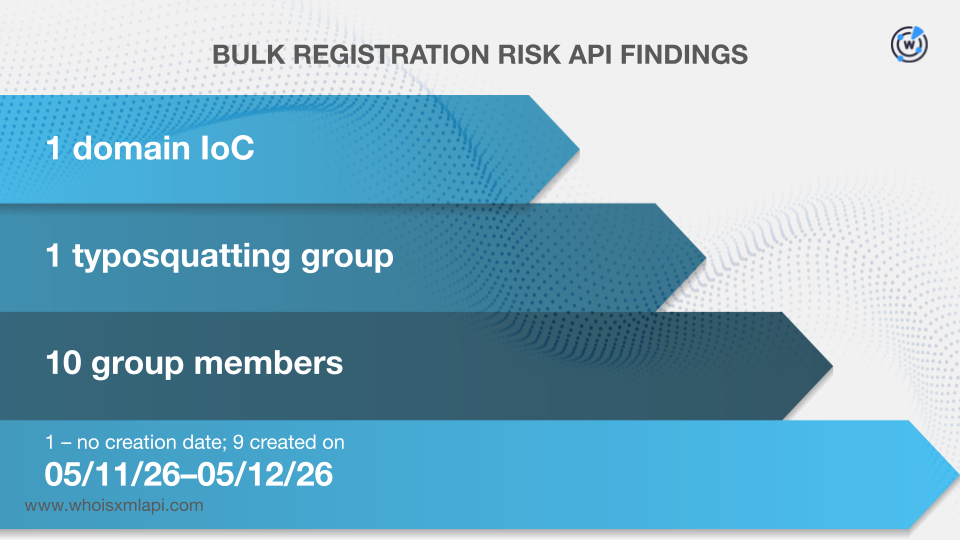
We queried the domain IoCs on Bulk Registration Risk API next and found out that wa-connect[.]net appeared in a typosquatting group along with nine lookalikes. While l-connect[.]io did not have a creation date, three domains (i.e., kmconnect[.]online, pmo-connect[.]com, and kmconnect[.]nl) were created on 11 May 2026 and the remaining six domains, including the IoC (i.e., ut-connect[.]net, msmconnect[.]org, go-connect[.]live, fm-connect[.]site, wa-connect[.]net, and gmo-connect[.]cloud) were created on 12 May 2026.
Next, we determined that the domain IoC miov2iaiaoubqosiqoiajwowiwjso[.]online appeared on the First Watch Malicious Domains Data Feed as soon as it was created on 20 November 2025, 274 days before GTIG dubbed it as an IoC.
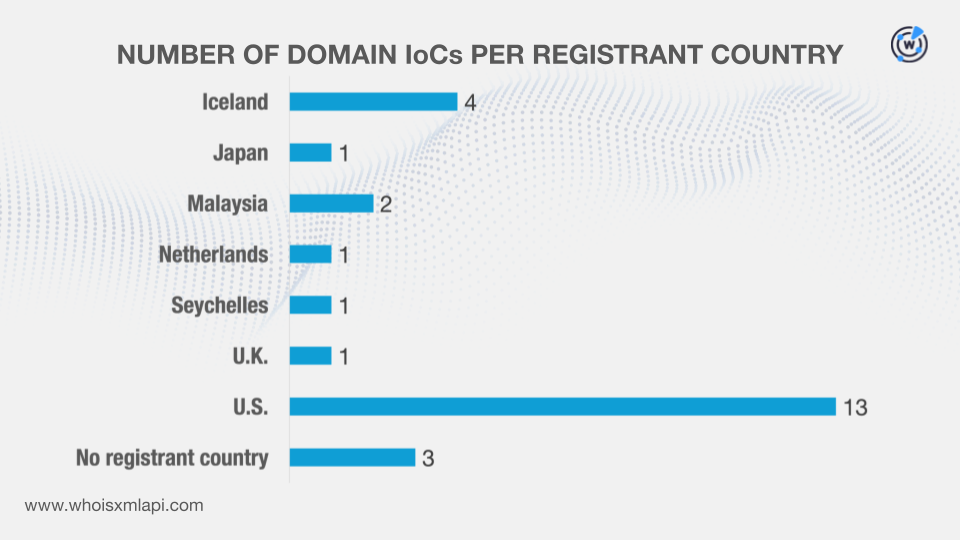
After that, we queried the domain IoCs on WHOIS API and discovered that:
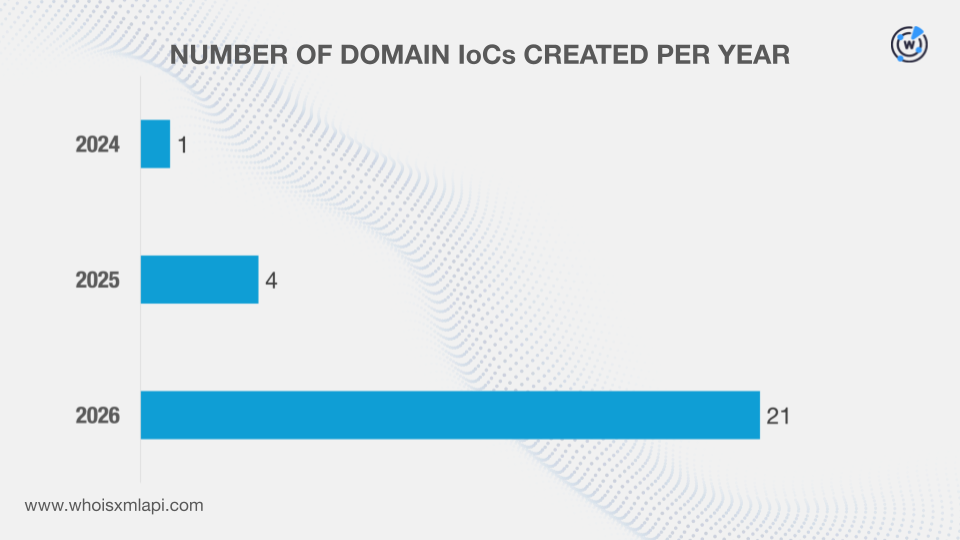
They were administered by seven registrars.
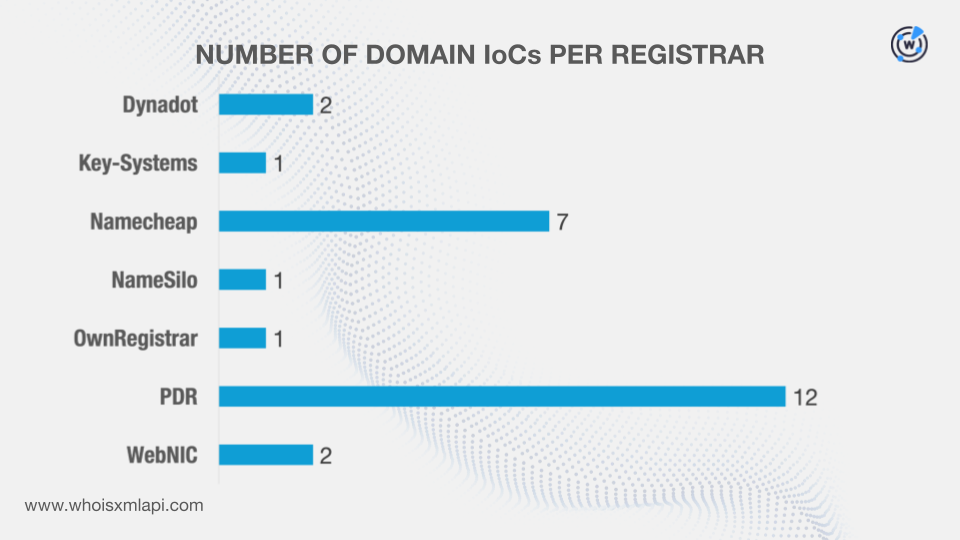
While three of them did not have registrant countries on record, the remaining 23 were registered in seven countries.
Finally, we queried the domain IoCs on DNS Chronicle API and learned that they recorded 614 historical domain-to-IP resolutions over time. Take a look at more information for five examples below.
| DOMAIN IoC | NUMBER OF DOMAIN-TO-IP RESOLUTIONS | DATES SEEN |
|---|---|---|
| globsec[.]net | 269 | 02/05/17–07/30/26 |
| kiis[.]co[.]uk | 120 | 02/06/17–07/29/26 |
| wa-meeting[.]com | 69 | 06/27/24–07/28/26 |
| mioisiskwowiwjowuwjwolab[.]club | 34 | 11/20/25–08/01/26 |
| dosportal[.]app | 30 | 11/22/25–08/17/26 |
Next, we dove deeper into the DNS infrastructure of the five IP IoCs. From sample network traffic data from the IASC, we learned that 317 unique IP addresses potentially owned by victims communicated with the IP IoCs between 5 April to 23 August 2026. They were under 23 distinct ASNs.
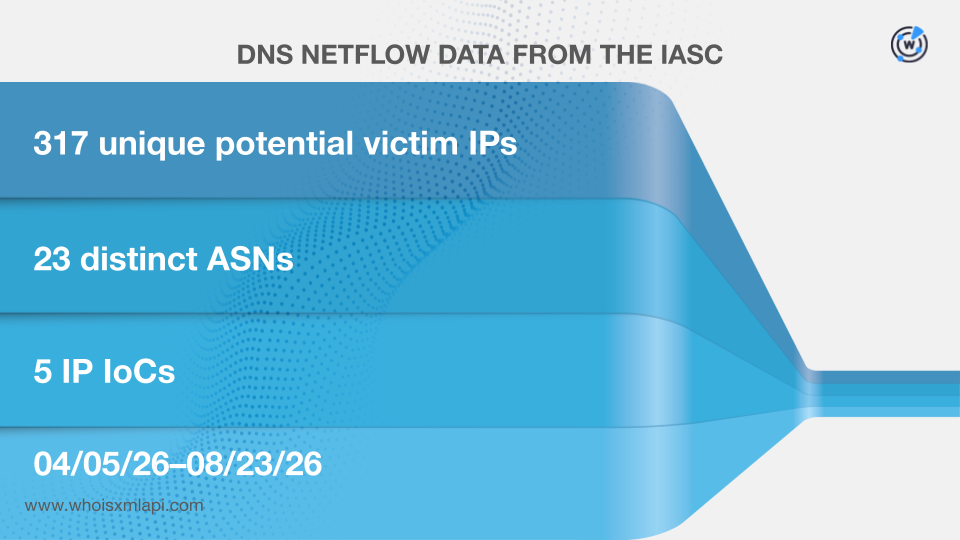
We then queried the IP IoCs on Bulk IP Geolocation Lookup and discovered that:
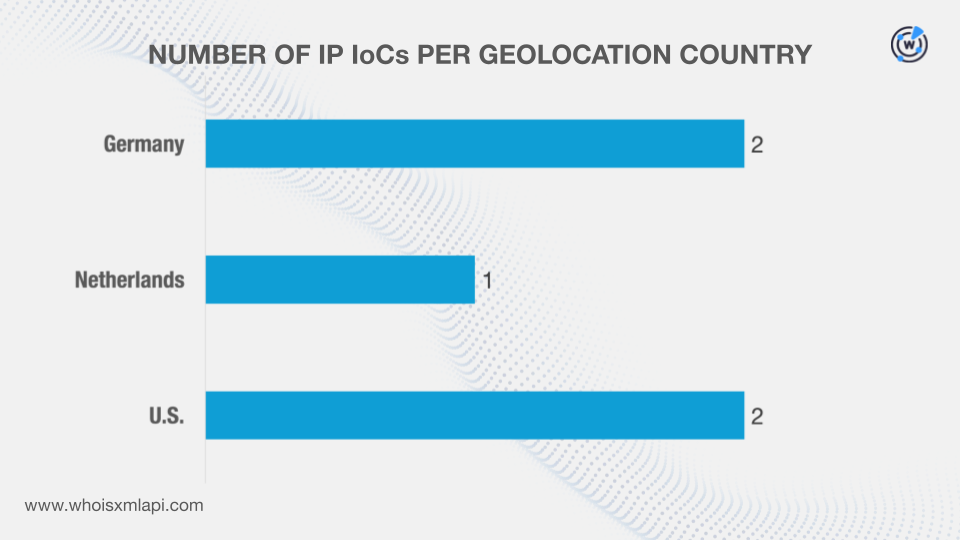
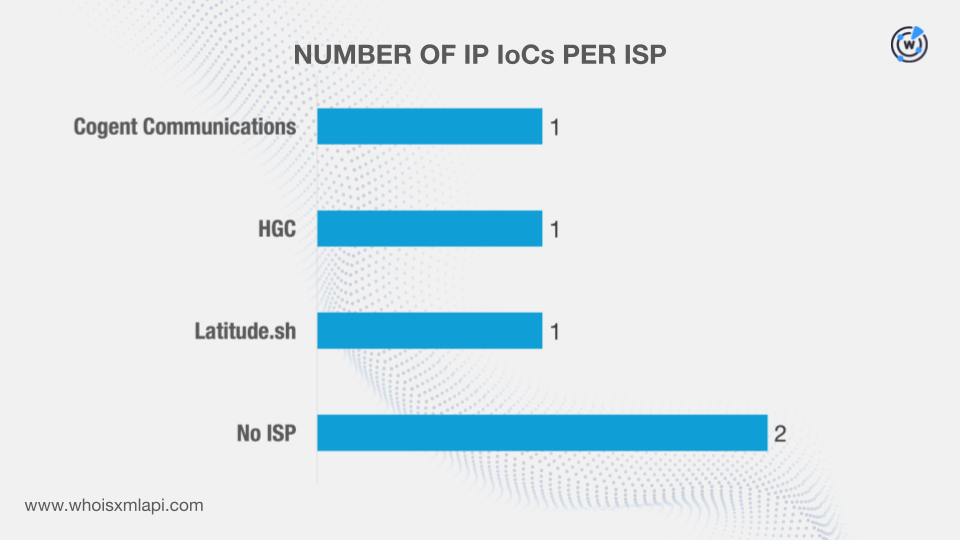
While two IP addresses did not have ISPs on record, each of the remaining three was administered by a different ISP.
We also queried the IP IoCs on DNS Chronicle API and found out that they posted 437 IP-to-domain resolutions over time. The IoC 104[.]194[.]159[.]150, for instance, recorded 385 resolutions from 16 August 2019 to 17 July 2026.
First, we queried the domain IoCs on WHOIS History API and learned that 25 had 34 unique email addresses in their historical WHOIS records. Further scrutiny revealed that nine were public email addresses.
We queried the public email addresses on Reverse WHOIS API, which led to the discovery of 2,494 unique email-connected domains after those already dubbed as IoCs were filtered out.
Threat Intelligence API queries for the email-connected domains revealed that three have already been weaponized for attacks. An example is dsapdlqpwd[.]icu, which has been associated with malware distribution between 26 April and 25 August 2026.
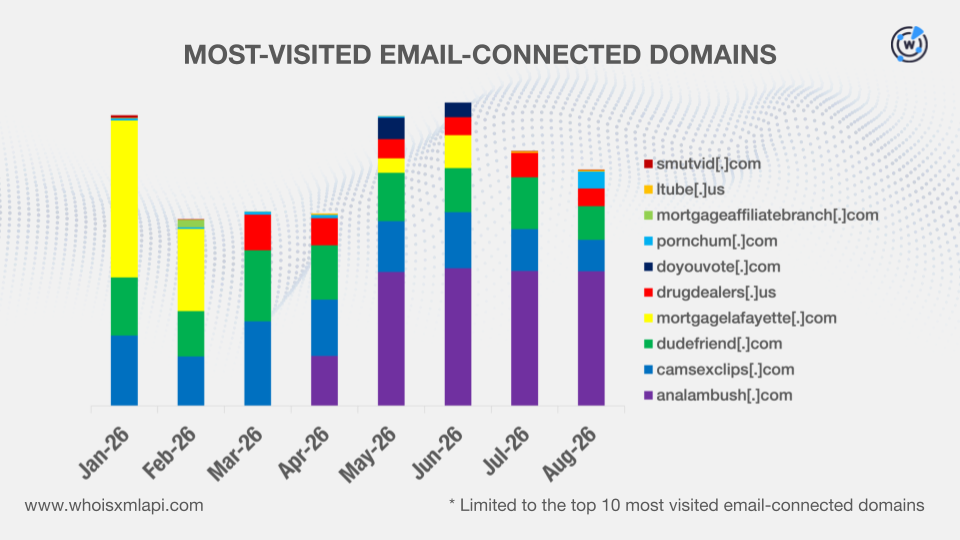
We also queried the email-connected domains on Domain Traffic API and identified the 10 with the highest number of visits since 1 January 2026.
This post only contains a snapshot of the full research. Download the complete findings and a sample of the additional artifacts on our website or contact us to discuss your intelligence needs for threat detection and response or other cybersecurity use cases.
Disclaimer: We take a cautionary stance toward threat detection and aim to provide relevant information to help protect against potential dangers. Consequently, it is possible that some entities identified as “threats” or “malicious” may eventually be deemed harmless upon further investigation or changes in context. We strongly recommend conducting supplementary investigations to corroborate the information provided herein.
Sponsored byRadix

Sponsored byCSC
Sponsored byIPv4.Global

Sponsored byWhoisXML API

Sponsored byDNIB.com

Sponsored byVerisign

Sponsored byVerisign
A World-Renowned Source for Internet Developments. Serving Since 2002.