
Welcome:
Login
|
Sign Up
|
About CircleID
Follow:
|
|
|

|
||
|
||
Security.com recently published an analysis of a China-based hackers-for-hire group Jewelbug espionage con crypto fraud campaign that trailed their sights on victims across the Middle East and Asia. The attackers administered both campaigns from a single control panel. And as of publishing, the group’s victim database recorded 1 million+ implant check-ins and 580K+ stolen browser cookies in less than three months of active operations.
The researchers publicized 27 network IoCs comprising 10 subdomains, five domains, and 12 IP addresses. We extracted unique domains from the subdomain IoCs then determined if any were owned by legitimate companies aided by the WhoisXML API MCP Server. We ended up with 10 domains; adding those to the 10 subdomains and 12 IP addresses identified as IoCs, we had 32 network IoCs in all for our DNS deep dive.
Our investigation led to these discoveries:
A sample of the additional artifacts obtained from our analysis is available for download from our website.
We kicked off our analysis by scrutinizing the 10 subdomain IoCs. We queried them on several of our tools via the WhoisXML API MCP Server. Take a look at more information on five of them below.
| SUBDOMAIN IoC | WXA MCP SERVER FINDING |
|---|---|
| browser-update[.]pages[.]dev | Despite being hosted on a legitimate apex domain, it was a confirmed malware host, specifically associated with a SocGholish-style fake browser update lure hosted on free Cloudflare pages. |
| eastus2[.]wac-azure[.]com | It was designated suspicious since it could be mimicking the Microsoft Azure domain. |
| fonts[.]chrorne[.]com | It was designated suspicious since it could be abusing the Chrome brand. |
| d2nq35tel3ucuo[.]cloudfront[.]net | Despite being hosted on a legitimate apex domain, it was dubbed a malware distributor. |
| ns1[.]jkskhei[.]com | It was tagged as malicious and could be imitating a nameserver. |
It is also interesting to note that the subdomain IoCs could be categorized into three clusters described in greater detail below.
| SUBDOMAIN IoC CLUSTER | SUBDOMAIN IoCs | RISK ASSESSMENT |
|---|---|---|
| Reputable cloud platform abuse | browser-update[.]pages[.]dev; d2nq35tel3ucuo[.]cloudfront[.]net; pub-abfa7742e315485a98a5fafd6dbfb68e[.]r2[.]dev; r6fi2yvqql.execute-api[.]ap-southeast-2[.]amazonaws[.]com | High risk; two were active malware hosts; two were considered suspicious |
| Namecheap + WithheldForPrivacy + Cloudflare | fonts[.]chrorne[.]com; ns1[.]jkskhei[.]com; robot[.]avbliud[.]com | High risk; shared operator tradecraft; one was an active malware host |
| Gname registrar | eastus2[.]wac-azure[.]com; fonts[.]tarotfree101[.]top; dns[.]wizkidblogger[.]com | Moderate to high risk; typosquatting or staging infrastructure |
Next, we looked more closely at the 10 domain IoCs. We began by querying them on WHOIS API and filling in gaps with data from Domain Info API. We discovered that:
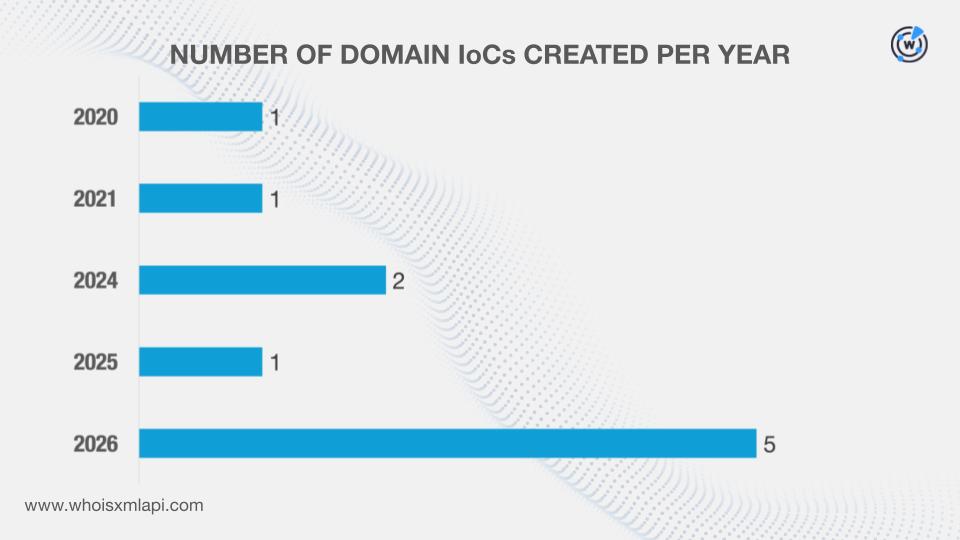
They were administered by five registrars.
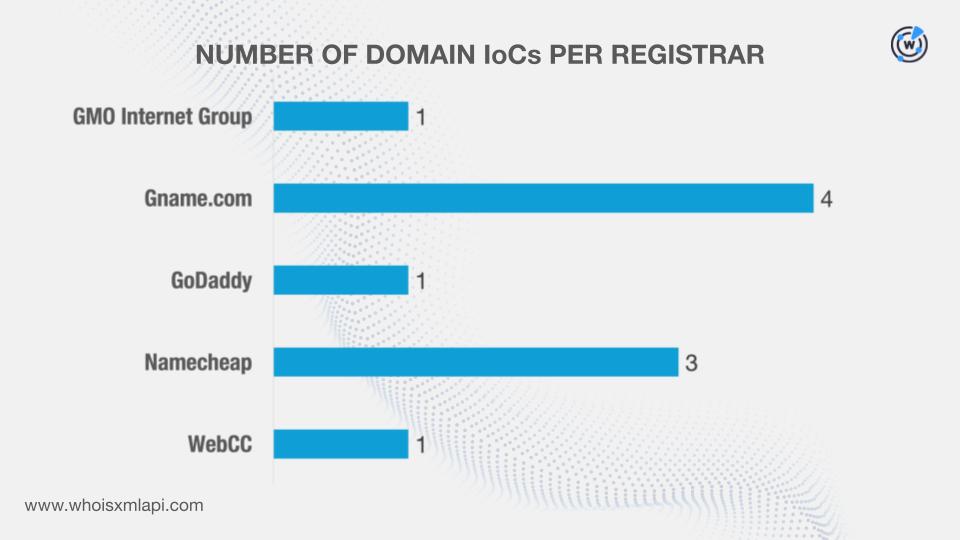
While one did not have a registrant country on record, the remaining nine were registered in three countries.
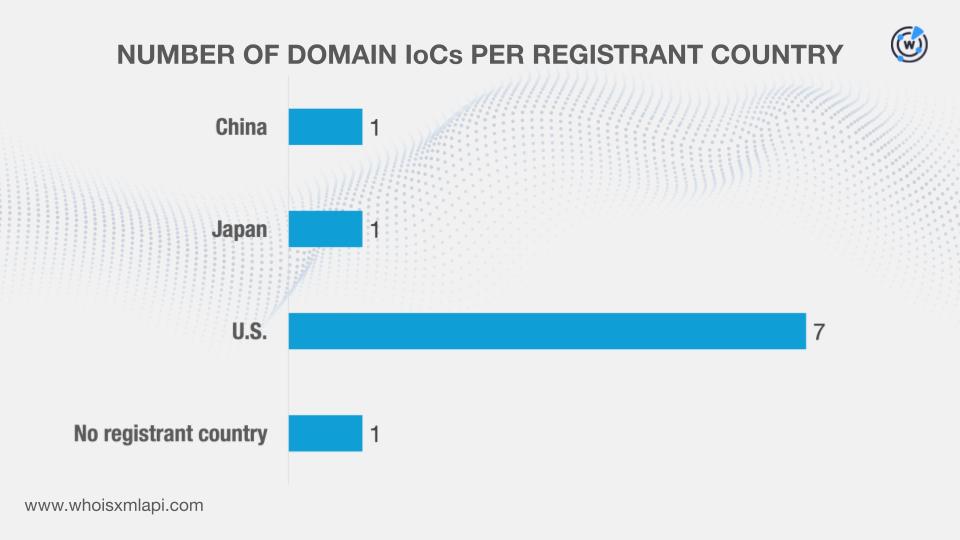
We then queried the domain IoCs on DNS Chronicle API and found out that eight recorded 898 historical domain-to-IP resolutions over time. Here are more details about five examples.
| DOMAIN IoC | NUMBER OF DOMAIN-TO-IP RESOLUTIONS | DATES SEEN |
|---|---|---|
| wizkidblogger[.]com | 338 | 02/07/17–06/30/25 |
| mailbycloud[.]com | 304 | 02/06/17–03/10/25 |
| wps-cn[.]com | 149 | 03/29/17–08/12/26 |
| f1ash[.]org[.]cn | 53 | 11/12/21–12/13/25 |
| wac-azure[.]com | 24 | 12/10/25–07/16/26 |
At least three of the domains had resolutions dating as far back as 2017. They may have been reregistered to become part of the threat infrastructure.
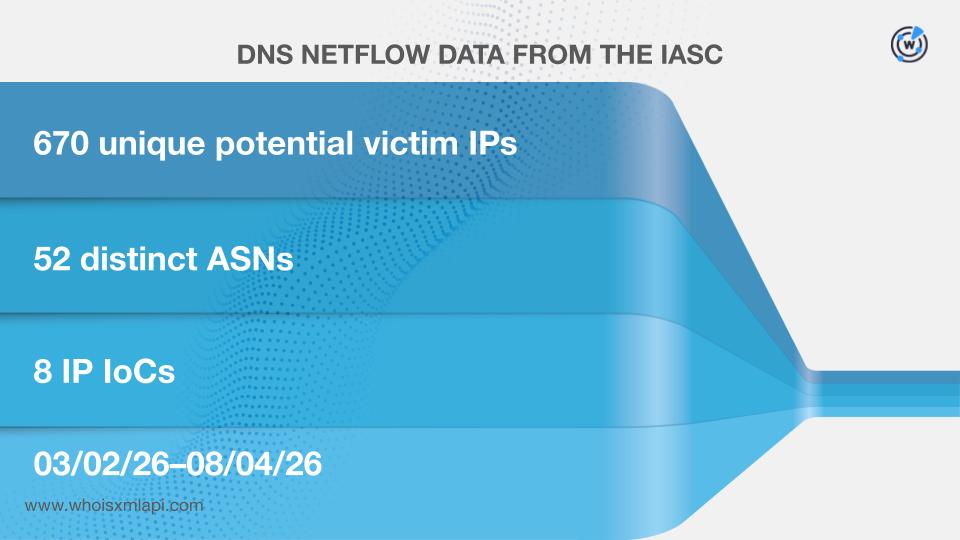
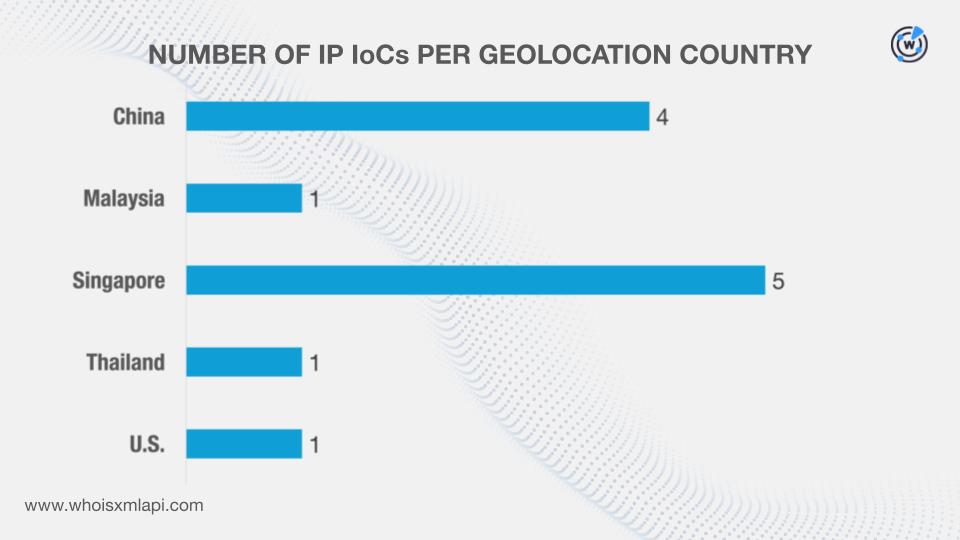
Next, we zoomed in on the 12 IP IoCs. First, sample network traffic data from the IASC revealed that 670 unique IP addresses potentially owned by victims under 52 distinct ASNs communicated with eight of the IP IoCs from 2 March to 4 August 2026.
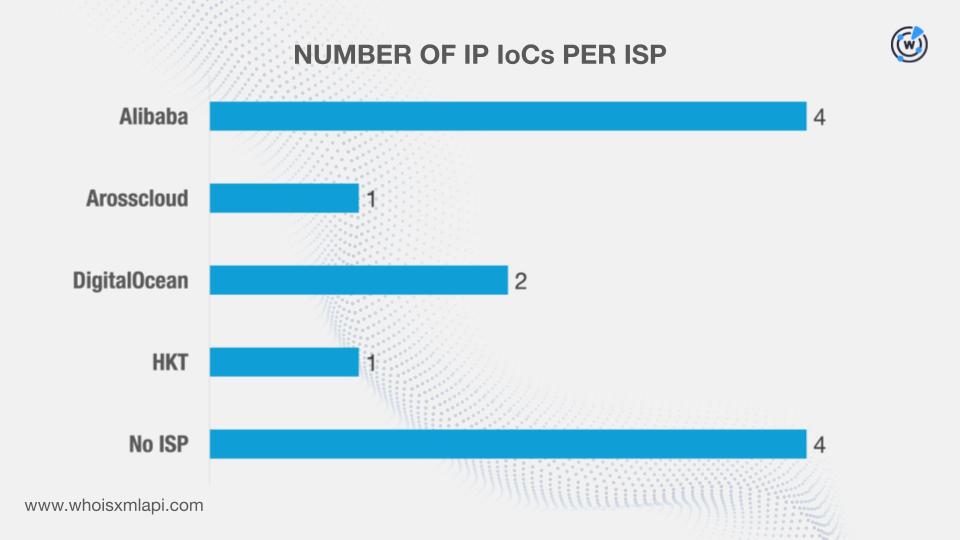
We then queried the IP IoCs on Bulk IP Geolocation Lookup and discovered that:
While four did not have ISPs on record, the remaining eight were administered by four ISPs.
After that, we queried the IP IoCs on DNS Chronicle API and found out that seven posted 1,566 historical IP-to-domain resolutions over time. Take a look at more information about five examples below.
| IP IoC | NUMBER OF IP-TO-DOMAIN RESOLUTIONS | DATES SEEN |
|---|---|---|
| 43[.]246[.]208[.]179 | 650 | 08/02/24–08/18/26 |
| 43[.]246[.]208[.]236 | 366 | 02/05/17–03/29/25 |
| 167[.]71[.]195[.]255 | 258 | 08/03/19–02/27/26 |
| 219[.]76[.]254[.]184 | 232 | 02/06/17–03/27/26 |
| 103[.]87[.]9[.]62 | 57 | 06/03/18–11/22/24 |
Several of the IP IoCs stopped recording resolutions before 2026.
Next, we scoured the DNS for artifacts that could be tied to the Jewelbug attack. First, we queried the domain IoCs on WHOIS History API. We learned that seven had 18 unique email addresses in their historical records.
Upon further scrutiny, we determined that 10 were public email addresses but one could potentially belong to a domainer. That said, we continued our analysis for only nine public email addresses. We queried them on Reverse WHOIS API, which led to the discovery of 5,331 distinct email-connected domains after those already dubbed as IoCs were filtered out.
We queried the email-connected domains on Threat Intelligence API and discovered that one—q-vpn[.]com—has already been weaponized to distribute malware since 27 January 2025.
We also queried the email-connected domains on Domain Traffic API and identified 10 with the highest number of visits.
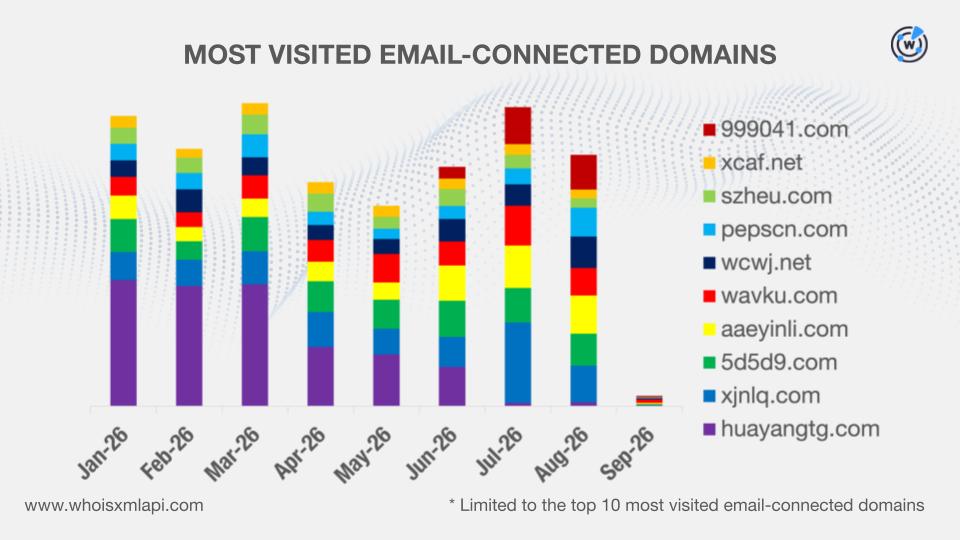
Check out more 2026 information about the 10 most visited email-connected domains below.
| EMAIL- CONNECTED DOMAIN | JAN | FEB | MAR | APR | MAY | JUN | JUL | AUG | SEP | TOTAL |
|---|---|---|---|---|---|---|---|---|---|---|
| huayangtg[.]com | 3,435 | 3,272 | 3,318 | 1,611 | 1,406 | 1,067 | 87 | 109 | 14 | 14,319 |
| xjnlq[.]com | 762 | 713 | 900 | 953 | 704 | 819 | 2,196 | 994 | 24 | 8,065 |
| 5d5d9[.]com | 900 | 508 | 930 | 836 | 791 | 985 | 938 | 874 | 20 | 6,782 |
| aaeyinli[.]com | 637 | 386 | 504 | 530 | 470 | 963 | 1,156 | 1,039 | 31 | 5,716 |
| wavku[.]com | 514 | 401 | 635 | 598 | 771 | 651 | 1,083 | 745 | 95 | 5,493 |
| wcwj[.]net | 445 | 629 | 488 | 408 | 409 | 612 | 584 | 858 | 25 | 4,458 |
| pepscn[.]com | 452 | 441 | 628 | 360 | 280 | 355 | 431 | 784 | 26 | 3,757 |
| szheu[.]com | 441 | 420 | 540 | 493 | 329 | 459 | 369 | 257 | 7 | 3,315 |
| xcaf[.]net | 322 | 237 | 308 | 313 | 300 | 285 | 294 | 242 | 7 | 2,308 |
| 999041[.]com | 0 | 0 | 0 | 0 | 0 | 321 | 1,010 | 941 | 29 | 2,301 |
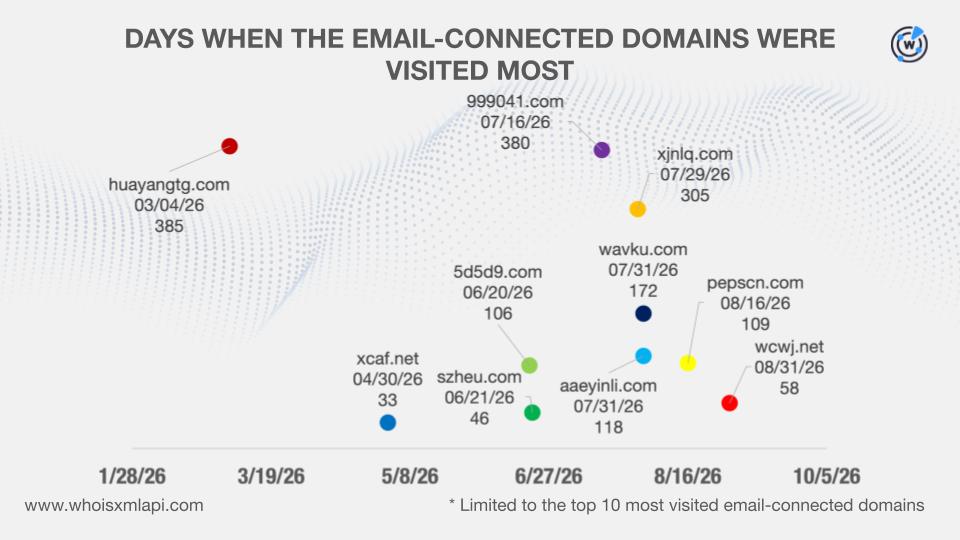
It is interesting to note that despite being seemingly DGA domains, the artifacts have been visited a lot even to this day. We also mapped out when each email-connected domain received the highest number of daily visits.
This post only contains a snapshot of the full research. Download the complete findings and a sample of the additional artifacts on our website or contact us to discuss your intelligence needs for threat detection and response or other cybersecurity use cases.
Disclaimer: We take a cautionary stance toward threat detection and aim to provide relevant information to help protect against potential dangers. Consequently, it is possible that some entities identified as “threats” or “malicious” may eventually be deemed harmless upon further investigation or changes in context. We strongly recommend conducting supplementary investigations to corroborate the information provided herein.
Sponsored byCSC
Sponsored byWhoisXML API

Sponsored byIPv4.Global

Sponsored byRadix

Sponsored byDNIB.com

Sponsored byVerisign

Sponsored byVerisign
A World-Renowned Source for Internet Developments. Serving Since 2002.