
Welcome:
Login
|
Sign Up
|
About CircleID
Follow:
|
|

|
||
|
||
Microsoft recently investigated a high-volume phishing campaign that used invisible Unicode tag characters, a technique popularized in AI prompt injection research as “ASCII smuggling.” Instead of using these characters to hide instructions from people while exposing them to AI models, the attacker used them to split financial lure words like “funding” to prevent email filters from parsing them.
The researchers identified 45 network IoCs comprising 20 domains and 25 IP addresses related to the threat. We confirmed that none of the domain IoCs were owned by legitimate entities using the WhoisXML API MCP Server so we proceeded with our analysis that led to these discoveries:
Note that while Microsoft identified 148 phishing domains in all, they only published 20 in their report. We analyzed the sample domains and in the end collated 165 connected artifacts, 158 of which have not been detected by any of the engines listed on VirusTotal.
A sample of the additional artifacts obtained from our analysis is available for download from our website.
We kicked off our investigation by looking more closely at the 20 domain IoCs.
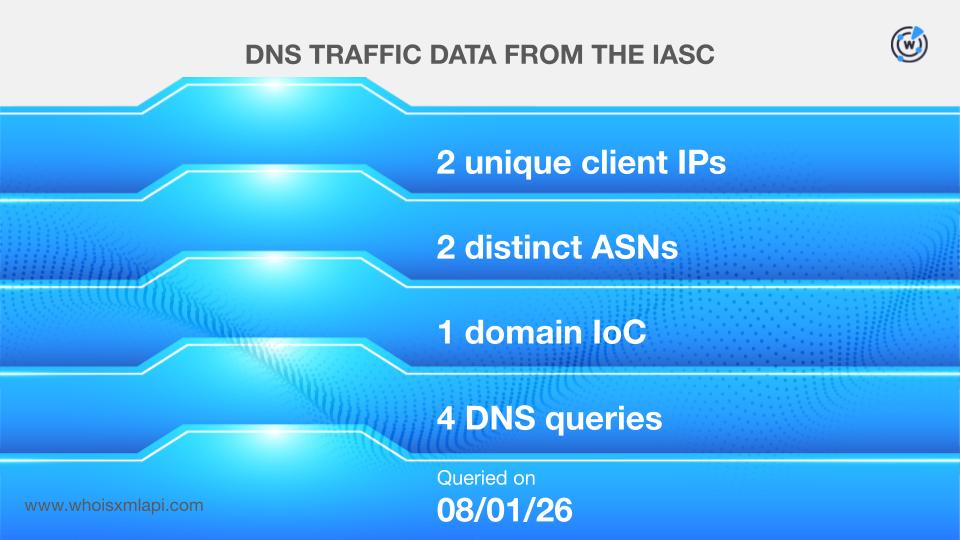
First, sample network traffic data from the IASC revealed that two unique client IP addresses under two ASNs communicated with the domain IoC directcapitalboost[.]com via four DNS queries on 1 August 2026.
Using data from the First Watch Malicious Domains Data Feed, we discovered that five of the domain IoCs were likely registered with malicious intent between 345 and 630 days before Microsoft identified them as IoCs on 3 September 2026. Take a look at more information for three examples below.
| DOMAIN IoC | FIRST WATCH DATE | NUMBER OF DAYS BEFORE THE REPORT DATE |
|---|---|---|
| digitalcapitalboost[.]com | 12/12/24 | 630 |
| fundingexpresscapital[.]com | 09/03/25 | 365 |
| guardiancapitalway[.]com | 09/03/25 | 365 |
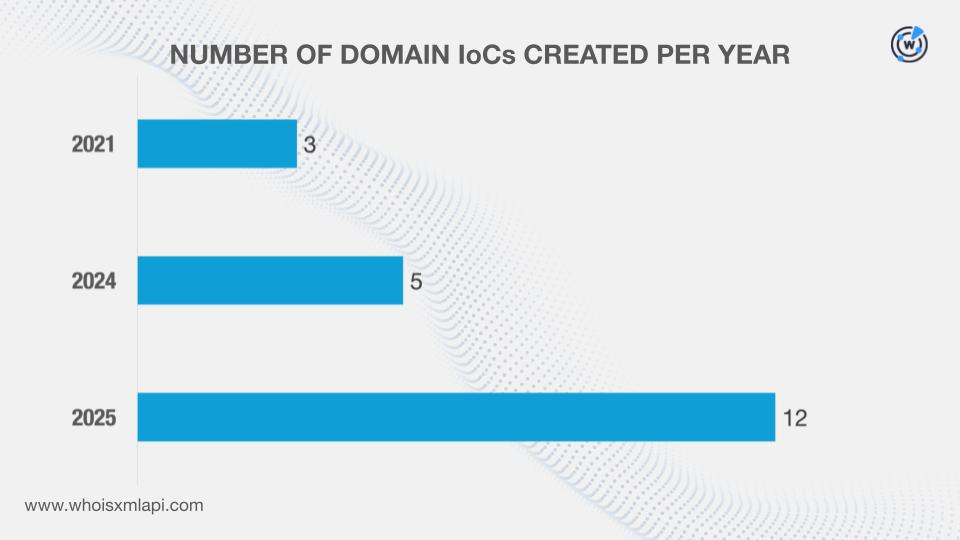
Next, we queried the domain IoCs on WHOIS API and learned that:
Finally, we queried the domain IoCs on DNS Chronicle API and found out that they recorded 2,292 historical domain-to-IP resolutions over time. Here are more details for five examples.
| DOMAIN IoC | NUMBER OF DOMAIN-TO-IP RESOLUTIONS | DATES SEEN |
|---|---|---|
| ourbusinessloans[.]com | 329 | 02/06/17–09/02/26 |
| digitalcapitalboost[.]com | 251 | 12/22/24–09/06/26 |
| onlinedirectfinance[.]com | 242 | 05/21/21–08/20/26 |
| harboradvancefunding[.]com | 140 | 01/28/25–08/30/26 |
| advancefundingboost[.]com | 127 | 12/03/24–08/25/26 |
Next up, we investigated the 25 IP IoCs further.
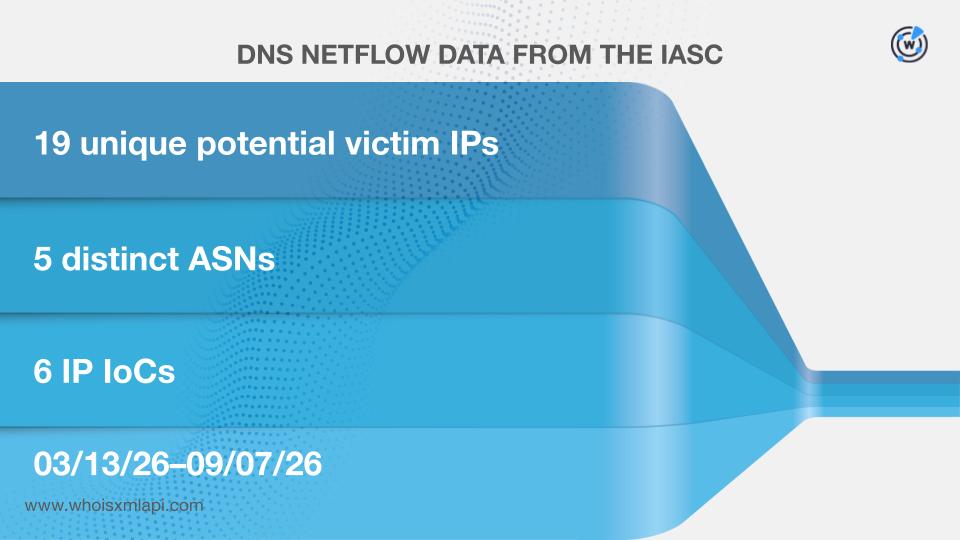
First, sample network traffic data from the IASC revealed that 19 unique IP addresses that could belong to victims communicated with six of the IP IoCs between 13 March and 7 September 2026. They fell under five distinct ASNs.
We then queried the IP IoCs on Bulk IP Geolocation Lookup and discovered that they were all geolocated in the U.S. although their ISPs were not named.
The results of our DNS Chronicle API queries for the IP IoCs, meanwhile, showed that 23 of them posted 9,264 historical IP-to-domain resolutions over time. Take a look at more information for five examples below.
| IP IoC | NUMBER OF IP-TO-DOMAIN RESOLUTIONS | DATES SEEN |
|---|---|---|
| 173[.]236[.]20[.]2 | 1,000 | 02/05/17–08/22/26 |
| 173[.]236[.]20[.]23 | 1,000 | 02/05/17–06/07/26 |
| 173[.]236[.]20[.]7 | 976 | 02/05/17–09/07/26 |
| 173[.]236[.]20[.]10 | 578 | 02/13/17–09/08/26 |
| 173[.]236[.]20[.]13 | 450 | 02/06/17–06/13/26 |
Next, we kicked off our search for new artifacts.
First, we queried the domain IoCs on WHOIS History API and discovered that one had a public email address in a historical WHOIS record.
We then queried the public email address on Reverse WHOIS API and uncovered 137 unique email-connected domains after those already dubbed as IoCs were filtered out.
According to data obtained from Domain Traffic API, three email-connected domains recorded six visits since 1 January 2026.
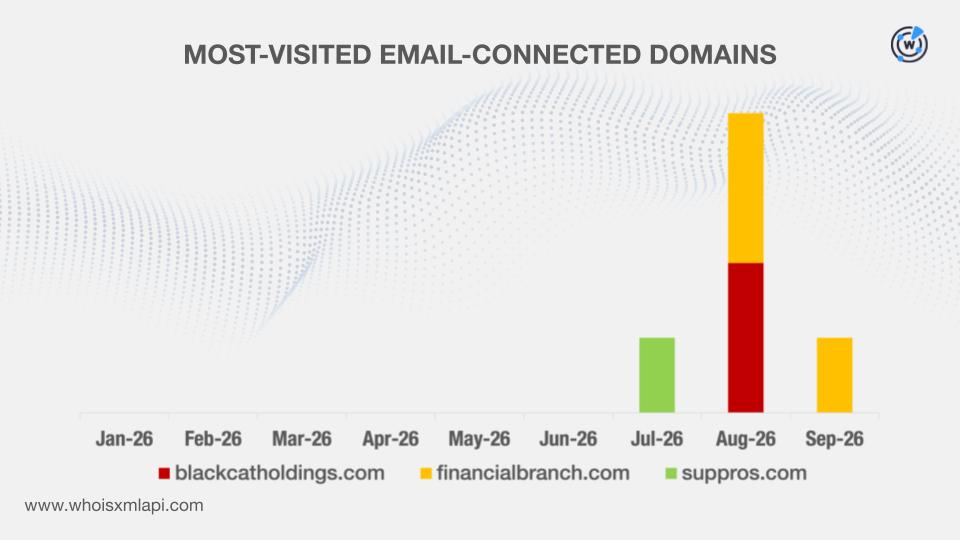
Here are more details about the most visited email-connected domains.
| EMAIL-CONNECTED DOMAIN | JAN | FEB | MAR | APR | MAY | JUN | JUL | AUG | SEP | TOTAL |
|---|---|---|---|---|---|---|---|---|---|---|
| blackcatholdings[.]com | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 2 | 0 | 2 |
| financialbranch[.]com | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 2 | 1 | 3 |
| suppros[.]com | 0 | 0 | 0 | 0 | 0 | 0 | 1 | 0 | 0 | 1 |
This post only contains a snapshot of the full research. Download the complete findings and a sample of the additional artifacts on our website or contact us to discuss your intelligence needs for threat detection and response or other cybersecurity use cases.
Disclaimer: We take a cautionary stance toward threat detection and aim to provide relevant information to help protect against potential dangers. Consequently, it is possible that some entities identified as “threats” or “malicious” may eventually be deemed harmless upon further investigation or changes in context. We strongly recommend conducting supplementary investigations to corroborate the information provided herein.
Sponsored byRadix

Sponsored byVerisign

Sponsored byDNIB.com

Sponsored byWhoisXML API

Sponsored byIPv4.Global

Sponsored byVerisign
Sponsored byCSC
A World-Renowned Source for Internet Developments. Serving Since 2002.