
Welcome:
Login
|
Sign Up
|
About CircleID
Follow:
|
|
|

|
||
|
||
Microsoft recently tracked a malware campaign that uses fake software download sites to impersonate trusted vendors and distribute malicious installers. They zoomed in on users looking for popular software but instead ended up with compromised organizations. While the attack primarily affected the China-based operations of multinational organizations, Chinese-speaking users should also be wary.
The researchers assessed with moderate confidence that the threat is consistent with previously reported Silver Fox fake software campaigns though it has not been attributed to any nation-state actor. They also identified network IoCs in their report.
While we obtained seven domain IoCs from the Microsoft report, we only analyzed six since one was owned by a legitimate entity based on the results of our checks via the WhoisXML API MCP Server. Adding that to the subdomain and two IP addresses in the original IoC list, we investigated nine network IoCs in all.
Our investigation led to these discoveries:
A sample of the additional artifacts obtained from our analysis is available for download from our website.
We first took a closer look at the sole subdomain IoC to kick off our investigation. Do note, however, that it is hosted on a legitimate apex domain that has no Threat Intelligence API hits based on the results of our WhoisXML API MCP Server query.
In addition, It is hosted on an IP address with 89 other subdomains. Here is a breakdown.
| APEX DOMAIN | NUMBER OF HOSTNAMES | DESCRIPTION |
|---|---|---|
| aliyuncs[.]com | 43 | The subdomain queried belonged to this group |
| thepacificlmc[.]com | 11 | Third-party hosting/site builder |
| thepacificxxs[.]com | 8 | Third-party hosting/site builder |
| thepacificphs[.]com | 7 | Third-party hosting/site builder |
| thepacificmax[.]com | 7 | Third-party hosting/site builder |
| thepacificwsu[.]com | 6 | Third-party hosting/site builder |
| thepacificgls[.]com | 5 | Third-party hosting/site builder |
| glacier[.]mba | 1 | Custom domain |
| yuelei-hf[.]com | 1 | Custom domain |
These hostnames were first seen as far back as 12 August 2025.
We then zoomed in on the six domain IoCs.
First, we queried them on Bulk Registration Risk API and discovered that two domain IoCs appeared in two separate typosquatting groups. One had two lookalikes while the other had three.
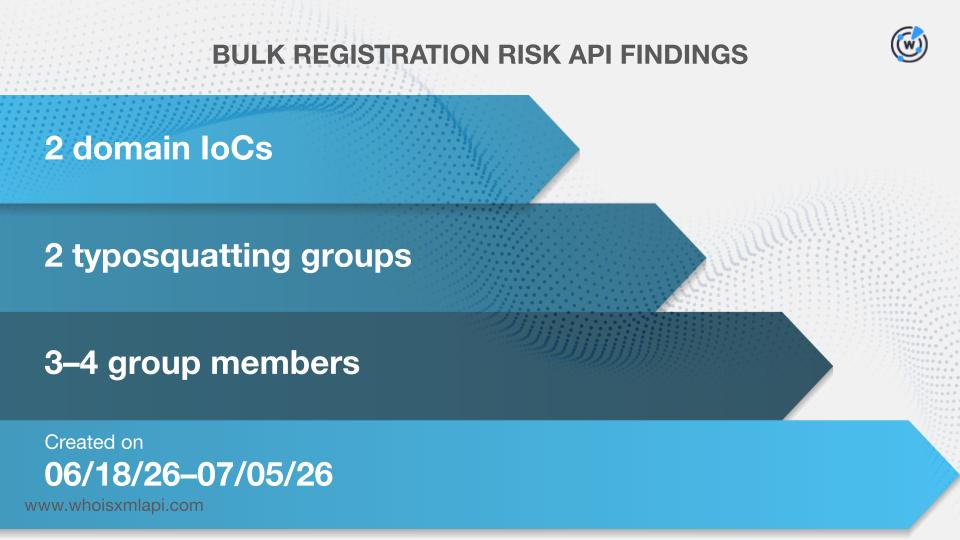
Here are more details about the typosquatting groups.
| DOMAIN IoC | GROUP NUMBER ID | GROUP MEMBER NUMBER | GROUP MEMBERS OTHER THAN THE IoCs | CREATION DATE |
|---|---|---|---|---|
| app-microsoft-edge[.]com[.]cn | 9993 | 3 | web-microsoft-edge[.]com[.]cn pc-microsoft-edge[.]com[.]cn | 06/18/26 |
| pc-razerzone[.]com[.]cn | 4024 | 4 | app-razerzone[.]com[.]cn zh-razerzone[.]com[.]cn an-razerzone[.]com[.]cn | 07/05/26 |
We also learned that one domain IoC—oijfwe[.]net—was likely registered with malicious intent. It appeared on the First Watch Malicious Domains Data Feed 781 days before being dubbed an IoC on 1 September 2026.
Next, we queried the domain IoCs on WHOIS API and found out that:
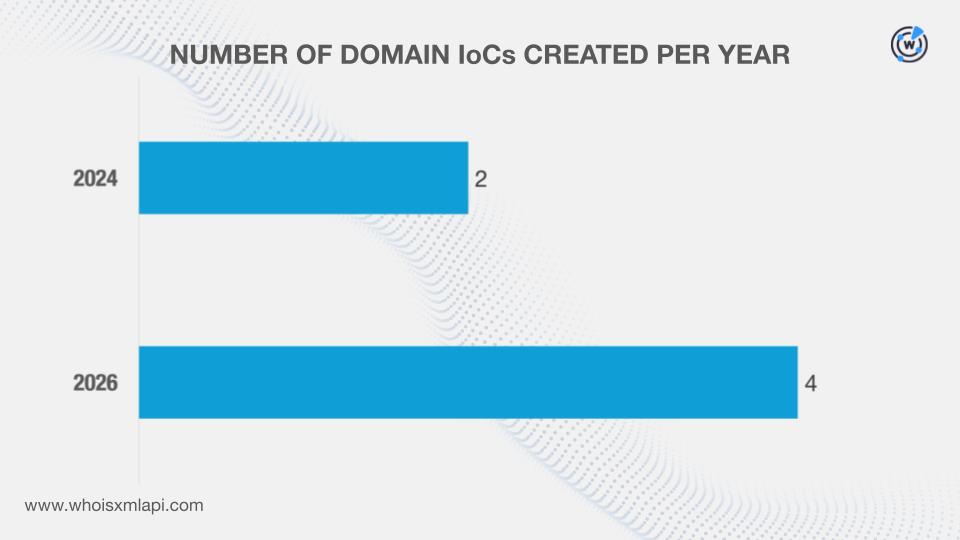
They were administered by four registrars.
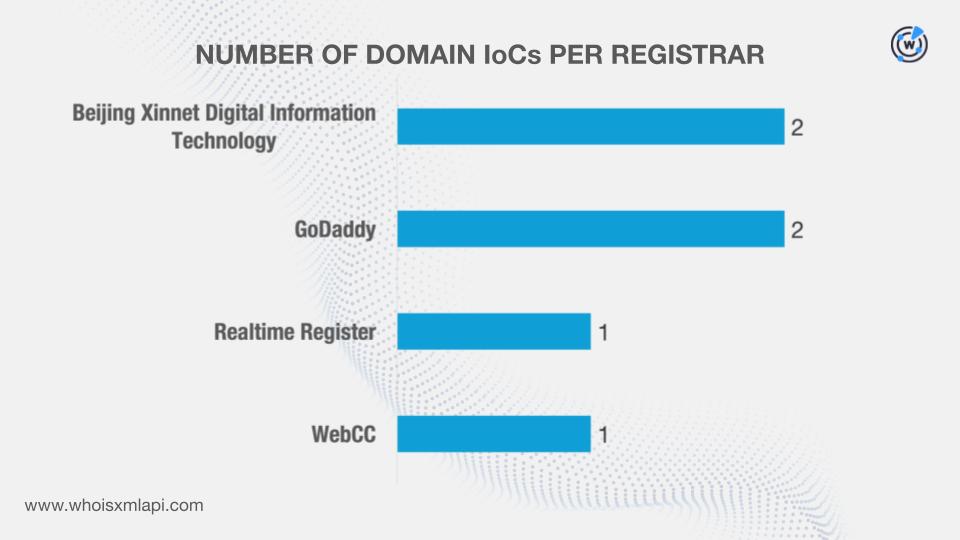
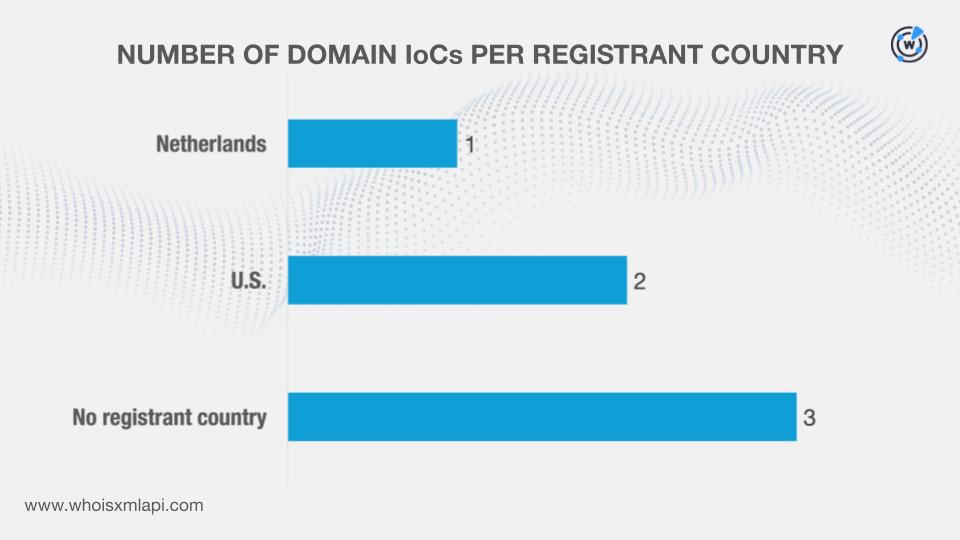
While three did not have registrant countries on record, the remaining three were registered in two countries.
Based on the results of our DNS Chronicle API queries for the domain IoCs, five recorded 98 historical domain-to-IP resolutions over time. Here are more details for three examples.
| DOMAIN IoC | NUMBER OF DOMAIN-TO-IP RESOLUTIONS | DATES SEEN |
|---|---|---|
| oijfwe[.]net | 52 | 07/14/24–08/28/26 |
| iualef[.]net | 36 | 07/14/24–08/22/26 |
| kaspersky-lab[.]hl[.]cn | 4 | 06/22/26–09/01/26 |
It is interesting to note that two domain IoCs that could have been created using DGA posted more resolutions than those riding on known software brands like kaspersky-lab[.]hl[.]cn.
Next up, we took a closer look at the two IP IoCs.
Sample network traffic data from the IASC showed that two potential victim IP addresses communicated with one of the IP IoCs between 9 and 20 June 2026.
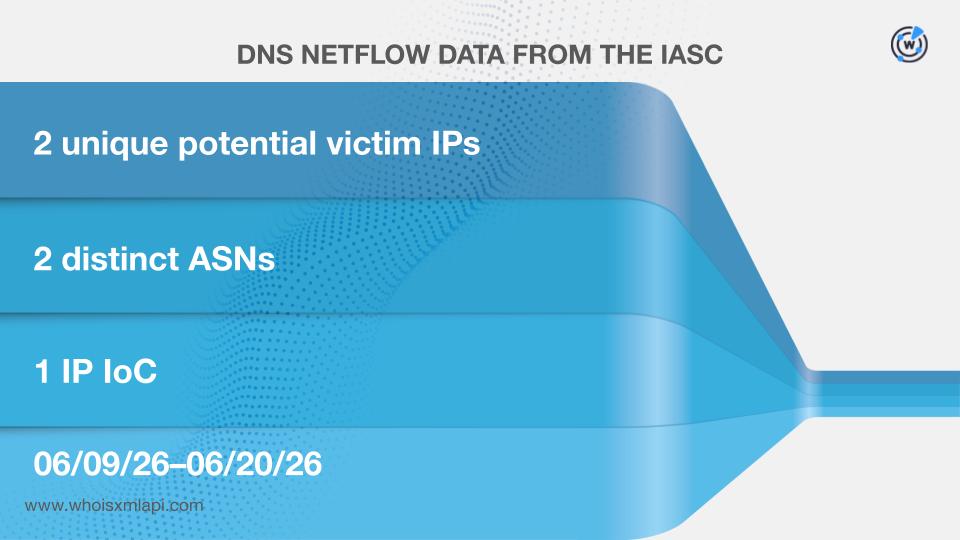
We then queried them on Bulk IP Geolocation Lookup and discovered that while they were both geolocated in China, they had different ISPs.
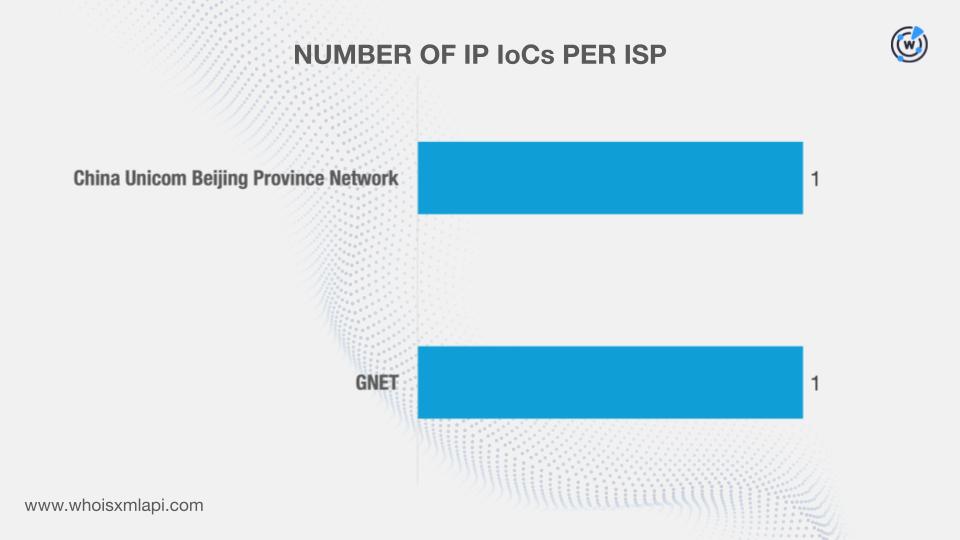
When queried on DNS Chronicle API and learned that they posted 1,005 historical IP-to-domain resolutions over time. The IP 202[.]95[.]14[.]237, for instance recorded 1,000 resolutions from 1 July 2019 to 3 December 2021.
To uncover new artifacts possibly connected to this fake installer campaign, we expanded the current list of IoCs.
We began by querying the domain IoCs on WHOIS History API and learned that three had three unique public email addresses in their historical records. This allowed us to unearth 1,474 distinct email-connected domains after those already named as IoCs were filtered out aided by Reverse WHOIS API.
According to the results of our Threat Intelligence API queries for the email-connected domains, five have already figured in malicious campaigns. An example is ai-claude[.]com[.]cn, which has been associated with malware distribution since 7 August 2026.
This post only contains a snapshot of the full research. Download the complete findings and a sample of the additional artifacts on our website or contact us to discuss your intelligence needs for threat detection and response or other cybersecurity use cases.
Disclaimer: We take a cautionary stance toward threat detection and aim to provide relevant information to help protect against potential dangers. Consequently, it is possible that some entities identified as “threats” or “malicious” may eventually be deemed harmless upon further investigation or changes in context. We strongly recommend conducting supplementary investigations to corroborate the information provided herein.
Sponsored byVerisign

Sponsored byDNIB.com

Sponsored byVerisign
Sponsored byIPv4.Global

Sponsored byWhoisXML API

Sponsored byRadix

Sponsored byCSC
A World-Renowned Source for Internet Developments. Serving Since 2002.